
Security, privacy and AI governance
Sensitive family information deserves professional-grade controls.
Succession Navigator is designed to keep each organisation’s data separated, give the right people the right access, preserve the source of important information and keep professional judgement in human hands.
Sydney
Current application, database and private storage region
2FA
Authenticator-app protection for the confirmed privileged scope
Tenant scoped
Organisation and case boundaries enforced on the server
Human controlled
AI proposes; authorised people decide
Infrastructure and data location
Hosted in Sydney.
The current Succession Navigator environment is hosted in DigitalOcean’s Sydney region. The application service, managed PostgreSQL database and private object storage are located in Sydney.
That is a statement about where the current environment runs. It is not a certification, a compliance approval, or a claim about who owns the underlying provider.
DigitalOcean, Sydney region
Application
DigitalOcean App Platform
Database
Managed PostgreSQL
Files
Private object storage
This describes the current environment. It is not a certification, a compliance approval or a guarantee beyond the infrastructure configuration described here.
Identity, roles and 2FA
Access follows the person, their role and the organisation they belong to.
Platform Administrator
Platform scope
Runs the platform itself. The narrowest group, and the scope where authenticator-app 2FA is active today.
Practice Administrator
Organisation scope
Manages one practice: its people, its clients and its settings. Cannot reach another organisation.
Adviser / Facilitator
Assigned organisation and cases
Works the cases they are assigned. Case access follows the assignment, not the job title.
Family participant
Narrow, scoped participation
Sees only what their own participation requires. No view of the adviser's workspace or internal notes.
Active now
Authenticator-app 2FA is active for the production-test Platform Administrator scope.
Available to enable
Organisation policies can require 2FA for covered Practice Administrator and Adviser / Facilitator accounts when deliberately enabled.
Tenant and privacy boundaries
Each organisation is its own boundary.
The question this section exists to answer is a simple one. Could another practice, or another family, see our information?
- Users operate inside their authorised organisation
- Advisers receive role-appropriate case access
- Family participants receive narrow case-specific access
- Internal adviser notes remain internal
- Cross-organisation access is denied
Practice A
- Their advisers
- Their client cases
- Their family participants
Practice B
- Their advisers
- Their client cases
- Their family participants
No path between the two. Cross-organisation access is denied on the server, not hidden in the interface.
Evidence integrity and AI control
AI helps organise and propose. It does not become the decision-maker.
Capture
Transcripts and attributed statements keep their source.
Structure
Facts, assumptions, changes and contradictions stay distinct.
Validate
Guardrails stop generated wording being presented as definitive professional advice.
Decide
Authorised advisers and family members control what progresses.
In the product
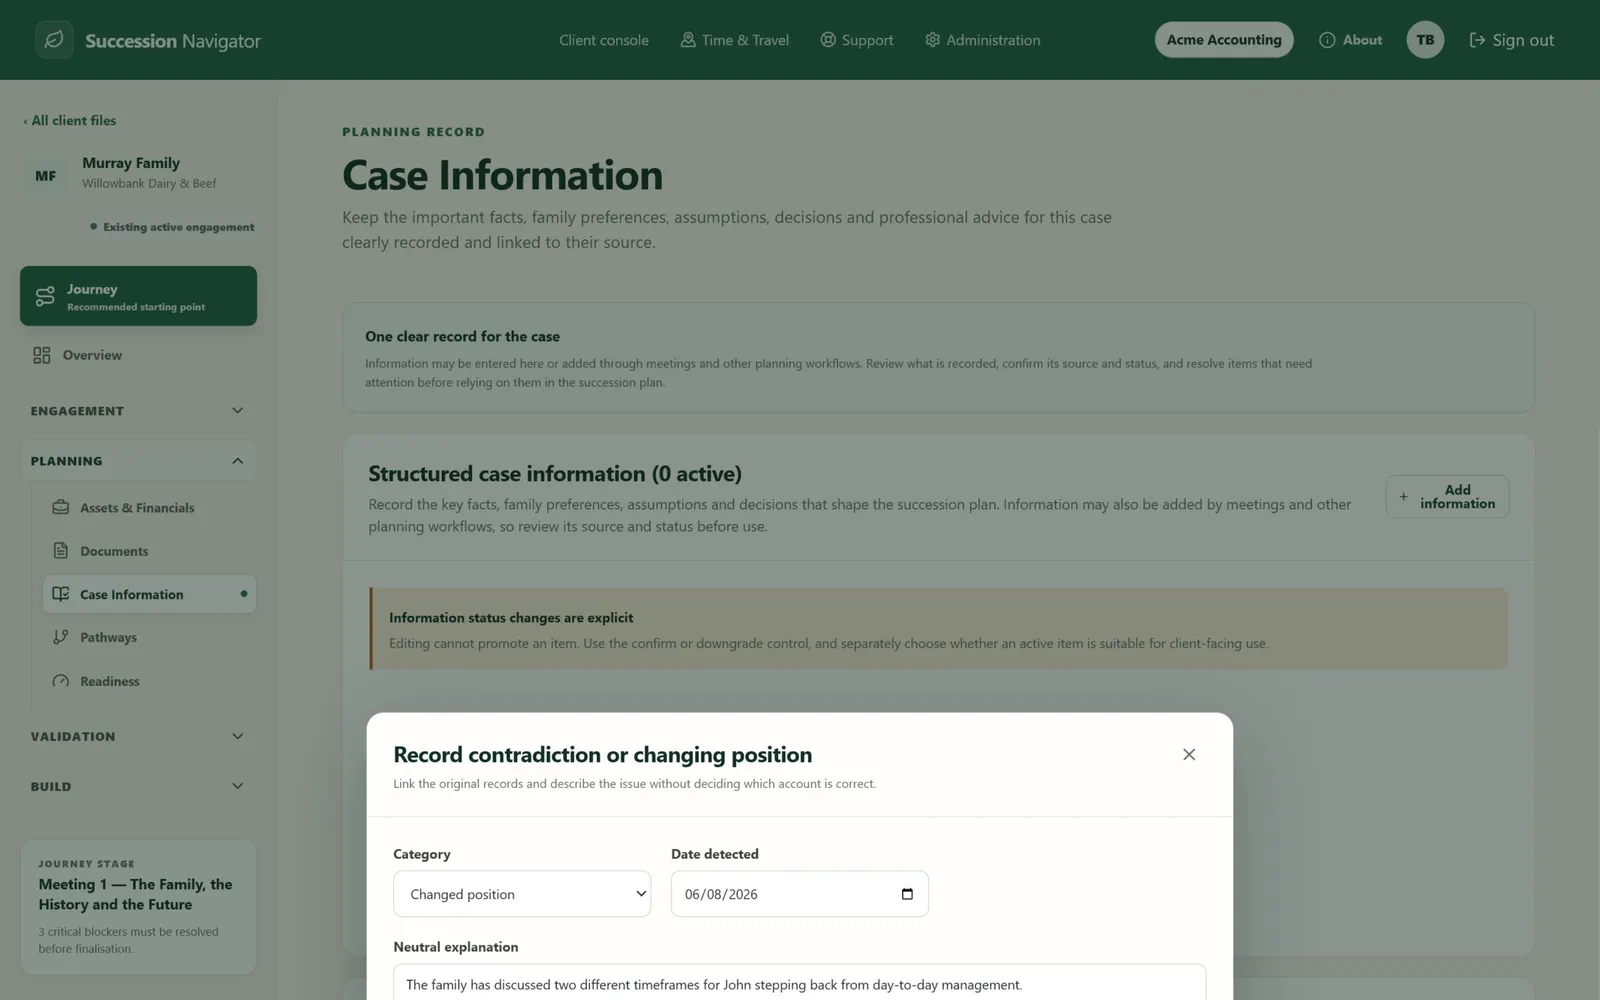
Record changed or conflicting information transparently
Succession conversations evolve, and family members do not always agree. The misalignment workflow lets advisers link differing statements, classify the issue and document an appropriate resolution path without deleting either source. This creates a fairer, more auditable record and helps important disagreements remain visible until they are genuinely addressed.
AI proposes. Humans decide.
Raw meeting transcripts are captured and locked. The AI never edits or overwrites the original wording. Anything it infers sits as a proposal until a facilitator reviews the source and approves it.
Fact and assumption are different things.
A participant's statement, an assumption, the facilitator's interpretation and a verified fact are stored as different kinds of record. A passing comment cannot quietly become a binding family decision.
Contradictions are preserved.
When a statement conflicts with something said earlier, the system holds both and flags the conflict. It does not pick one, average them, or let the later one overwrite the earlier. Resolving it is the adviser's job.
Definitive advice is blocked.
Text that reads as definitive legal, tax or financial advice is blocked from client-facing documents until a licensed professional signs off. The system fails closed.
The family tree comes from recorded data.
The genogram is plotted from database relationships, not generated as an image. That is why blended families, step-children and multiple generations come out structurally correct.
Internal notes stay internal.
Facilitator notes and unverified AI observations default to adviser-only visibility. Making something client-facing is a separate, deliberate action.
Current status
Say what is true today. Update it as the platform matures.
Security pages tend to describe an aspiration. This one separates what runs today from what can be switched on, and leaves the last column for what your practice tells us it needs next.
Confirmed
- Current application, managed database and private storage are in the Sydney region
- Authenticator-app 2FA is active for the production-test Platform Administrator scope
- Multi-factor authentication is active on the DigitalOcean control-plane account the platform runs in
Configurable
- Covered organisation-level privileged roles can be placed under a 2FA policy when enabled
- That policy can be extended past the privileged roles to the rest of an organisation's users
Roadmap
Security and platform work continues. If there is a control, a report, an export or an integration your practice needs, tell us. It goes on the list, and what partners ask for shapes what gets built next.
Bring us your security questions.
If something here is not specific enough for your due diligence, ask. A straight answer, including where the answer is still “not yet”, is more useful to both of us than a confident page.
A conversation about your practice, the opportunity in your farming client base, and whether it's worth taking further. .